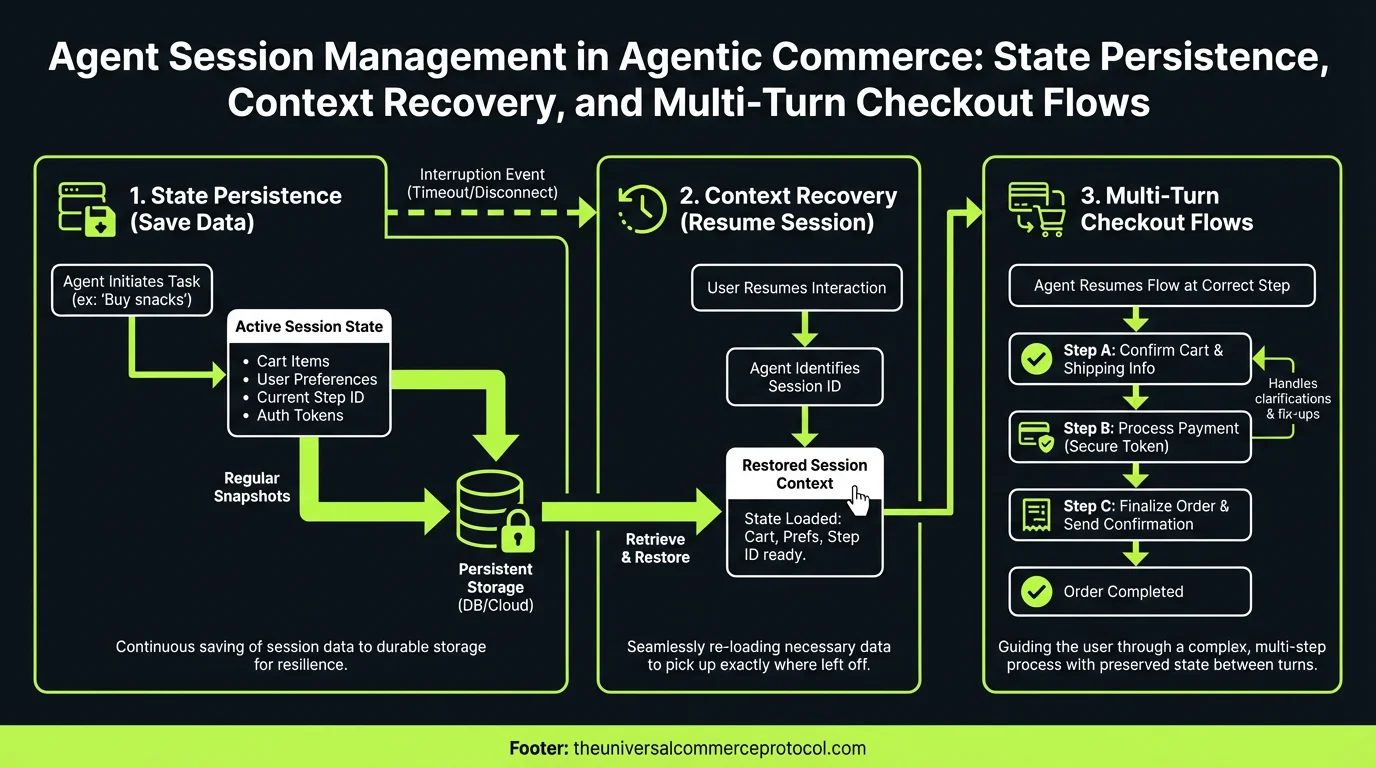
The Session Problem in Agentic Commerce
When a human visits an e-commerce site, session management is invisible—their cart persists, their preferences load, their payment method remembers them. When an AI agent conducts commerce on behalf of a consumer, session management becomes an operational necessity, not a convenience feature.
Unlike human shoppers who abandon and resume purchases hours or days later, agents execute commerce in seconds. But agents also face a unique problem: they operate across multiple API calls, fallback cycles, and potential interruptions. A network failure mid-checkout, a policy rejection requiring human approval, or a multi-day procurement process all demand robust session state.
Today, most agentic commerce implementations lack formal session architecture. Agents rebuild context on each retry. Merchants lose visibility into agent state when handoffs occur. Cross-device agent coordination (mobile agent, desktop agent, voice agent) creates duplicate purchase attempts.
What Session State Means for Agents
An agent session must capture:
- Shopping context: product selections, quantity, delivery address, special instructions
- Decision history: which payment methods were rejected, why approval workflows paused, what policy constraints apply
- Agent identity: which consumer the agent represents, which merchant credentials apply, authorization scope
- Temporal markers: when the session started, when each step completed, how long approval is valid
- Fallback state: which API endpoints have failed, which human interventions are pending, what retry logic is active
Without explicit session capture, agents re-query inventory for products already selected. They re-attempt payment methods that already failed. They lose track of partial approvals and require full re-authorization.
Session Persistence Architectures
Stateless Agent Design (Current Default)
Most deployed agents today run stateless: each call is independent, context is embedded in prompts, and state lives only in the consumer’s message history. This works for simple queries but breaks down in commerce:
- A payment failure forces the agent to re-explain the cart to a new human reviewer
- A multi-step approval workflow loses intermediate decisions
- Agents cannot be paused and resumed without losing optimization state
- No audit trail of agent reasoning across sessions
Session-Per-Transaction (Emerging Standard)
Forward-thinking platforms (Shopify agentic storefronts, JPMorgan/Mirakl implementations) assign each checkout a session ID. The session captures:
- Initial product manifest and pricing
- All policy checks applied (fraud, compliance, inventory hold)
- Each payment attempt and its result code
- Approval workflow state (pending, rejected, escalated)
- Timestamp and duration of each phase
On retry or resumption, the agent loads this session, updates only changed fields, and preserves all prior decision context. Merchants gain visibility into why a checkout paused.
Consumer-Persistent Sessions (Long-Term State)
Some merchants (particularly B2B platforms) maintain persistent agent sessions tied to a consumer profile. An agent can resume a purchase started three days earlier, re-validate the quote, and complete checkout without re-running the full recommendation engine.
This requires session storage with TTL policies: how long is a cart quote valid? How long should approval hold? When does session cleanup trigger?
Technical Implementation Patterns
Session Tokenization
A session token encodes: consumer ID, merchant ID, session start time, session version, and a cryptographic signature. Agents include this token in all API calls. Merchants validate the signature and reject stale sessions.
POST /checkout/session
X-Session-Token: eyJjb25zdW1lcl9pZCI6IjEyMzQ1IiwibWVyY2hhbnRfaWQiOiI2Nzg5MCIsInN0YXJ0X3RpbWUiOjE3NzM2NDAwMDAsInZlcnNpb24iOjF9.signature
Session State Versioning
As an agent updates cart contents or applies a discount, the session version increments. The merchant stores prior versions. On conflict (e.g., inventory changed mid-checkout), the agent can inspect version history and decide: re-validate the cart or escalate to the consumer.
Fallback-Aware Session Recovery
When an agent hits a fallback condition (payment declined, inventory unavailable, policy block), it writes a checkpoint to session state. On recovery, the agent can skip redundant steps:
Session State (Checkpoint):
- Cart validated ✓
- Inventory held ✓
- Shipping quoted ✓
- Payment attempt 1 failed (code: card_decline) ✗
- Next step: retry with alt payment method
The agent resumes at the next step, not the beginning of checkout.
Cross-Device Agent Coordination
If a consumer has multiple agents (voice on Alexa, mobile app, web chat), how do they coordinate a single purchase?
Naive approach: Each agent runs independently, creating duplicate orders.
Session-aware approach: The consumer’s session ID is visible to all agents. A voice agent can check: “Is a checkout in progress on mobile?” and either resume or decline to start a new one. Payment only processes once the consumer confirms across all active devices.
Session Lifecycle and Compliance
Sessions create audit records. Regulators (EU, UK FCA) expect merchants to prove how an AI agent made a decision. Session state provides that proof:
- What policies applied when the agent made this choice?
- Which inventory constraints were active?
- Did the agent receive approval before processing payment?
- How long did the consumer have to review before checkout completed?
Sessions also address PII retention requirements. A session can be flagged for deletion; merchants purge all session state after regulatory holds expire.
Session Timeout and Renewal
How long is a session valid? Too short, and agents fail on large orders. Too long, and inventory quotes become stale.
Industry practice (informed by payment industry PSD2 standards):
- Quote-level sessions: 5–15 minutes (product prices, availability)
- Approval-level sessions: 30 minutes (pending human review)
- Payment sessions: 3 hours (full checkout window)
- Consumer sessions: 24 hours (return and login context)
Agents should proactively refresh sessions nearing expiry, re-validating cart state before timeout triggers.
FAQ
Do I need session management if my agents only run one-shot checkouts?
Not immediately, but you lose observability. If a checkout fails and you want to offer consumers a resume option, session state is required. Shopify and JPMorgan both added this retroactively; building it in saves refactoring.
How does session management interact with PCI compliance?
Sessions should never store raw payment data. Instead, store a payment token reference and the token provider (Stripe, PayPal). The session records only that payment method X was attempted and failed with code Y.
Can an agent modify another agent’s session?
No. Sessions should include a session owner field. Only the agent that created the session can update it. A second agent attempting to resume must request a new session or get explicit consumer re-authorization.
What happens if inventory changes mid-session?
The merchant should write an inventory delta to the session: “2 units held at 2:14 PM UTC, 1 unit still available as of 2:19 PM.” The agent can inspect this and decide to confirm the order or re-quote the consumer.
How do session timeouts interact with agent approval workflows?
If a session expires while awaiting human approval, the agent should not proceed with payment. Instead, it should escalate: “Approval window expired. Consumer must re-authorize.” This forces fresh consent, not stale approval.
Should sessions be portable across merchants?
No. A session is merchant-specific. If an agent shops from multiple merchants in one purchase (e.g., a fulfillment agent buying from suppliers A and B), create separate sessions. Track them with a parent request ID so auditors can see the relationship.
How do I debug a failed agent checkout if I didn’t use sessions?
You have the consumer’s message history and your payment logs, but not the agent’s internal state. With sessions, you can replay: what did the agent see at each step? Why did it choose that payment method? Sessions cut debugging time from hours to minutes.
| Session Dimension | Legacy Cookie Session (Web 2.0) | UCP Cryptographic Agent Session | Session Hijack Risk | Session Duration / TTL | Enterprise Security |
|---|---|---|---|---|---|
Session Identifier |
Unencrypted plaintext cookie in browser storage |
Cryptographically signed JWT with ephemeral session keys | Zero Cookie Theft Exposure | Configurable 15m to 24h TTL | TLS 1.3 Strict Binding |
Device Binding |
Cookie copied across unauthorized machines |
Hardware-bound assertion tied to physical TPM / Secure Enclave | Zero Token Portability / Replay | Hardware Root of Trust | FIDO2 Device Attestation |
Concurrency |
Multiple browser tabs overwriting session data |
Optimistic concurrency locking with vector version stamps | Zero Concurrent Overwrite | Sub-millisecond Sync | Multi-Tab / Multi-Agent Safe |
Revocation |
Cookies remain valid until server expiration |
Instant sub-100ms revocation via distributed Redis blacklist | Zero Window of Vulnerability | < 100ms Revocation SLA | Instant Kill Switch |
Cross-Domain Mobility |
Third-party cookie blocking breaking cross-site sessions |
RFC 8615 well-known domain federation via mTLS | Zero Cross-Domain Breakage | Universal Domain Federation | Open Web Interoperability |
Audit Compliance |
Unlogged session access in generic web servers |
RFC 3161 timestamped immutable session audit trail | Zero Audit Ambiguity | SHA-256 Merkle Provenance | SOC 2 Type II Pass |
Developer & Enterprise FAQ
Q1: Why are browser session cookies incompatible with autonomous AI agents?
Agents operate in headless server environments without browser cookie jars, and cookies are blocked across domains by modern privacy protections; cryptographic tokens provide secure, portable session management.
Q2: How does device-bound session authentication stop session hijacking?
Tokens are mathematically bound to the private key stored inside the physical device’s Secure Enclave; even if an attacker intercepts the token, it cannot be signed or used on another machine.
Q3: How do merchants revoke compromised agent sessions across distributed edge servers?
By broadcasting a signed revocation notice to edge KV caches (like Cloudflare or Fastly), immediately blacklisting the session ID across all global gateways in under 100 milliseconds.
by
Tags:
Leave a Reply