Verifiable Intent is not a feature built inside the Universal Commerce Protocol. It is Mastercard’s framework, co-developed with Google, and it is protocol-agnostic: any commerce flow orchestrated through UCP can reference it, but UCP does not define it, sign it, or verify it with UCP keys.
That correction matters, because the job of Verifiable Intent is trust. In agentic commerce, conversational, stateless and often ambiguous agent interactions lack a visual checkout trail. There is no cart page to screenshot and no Place Order button to point to. Verifiable Intent turns an ambiguous request into an explicit, auditable approval that can be checked before fulfillment and reviewed afterwards.
Key takeaways
| Intent Dimension | Implicit Intent (Legacy Web) | Conversational Intent (Chatbots) | Verifiable Intent (UCP Standard) | Cryptographic Enabler | Legal Weight |
|---|---|---|---|---|---|
| User Authorization | Clicking an HTML button in a web browser. | Natural language prompt typed into a chat window. | Cryptographically signed W3C Verifiable Credential token. | FIDO AP2 WebAuthn biometric signature. | Irrefutable legal proof of explicit human delegation. |
| Constraint Bounding | Trusting frontend client-side JavaScript checks. | Prompt engineering hoping LLM honors spending limit. | Hardware-enforced mathematical budget caps & SKU whitelist. | Rich Authorization Requests (RFC 9396). | Absolute binding contract enforceable in court. |
| Non-Repudiation | User can claim accidental click or malware hijacked session. | User can claim chatbot hallucinated or misconstrued prompt. | Unforgeable digital signature generated inside hardware Secure Enclave. | Asymmetric private key attestation. | 100% liability shift from merchant to cardholder bank. |
| Revocation Semantics | Clearing browser cookies or logging out. | Typing ‘stop’ into conversation history. | Verifiable revocation entry in cryptographic ledger. | Append-only revocation registry. | Instant mathematical termination of agent spending power. |
| Audit Defense | Web server access logs and analytics pixels. | Proprietary chat conversation logs stored in database. | Self-contained signed transaction envelope verifying intent. | RFC 9421 cryptographic signature headers. | Certified tamper-evident record meeting SOC 2 & SEC standards. |
- Verifiable Intent establishes trust and accountability by linking an agent action to an explicit, signed statement of what the user approved.
- It keeps actions aligned with user intentions, requiring clear presentation and explicit approval before significant actions proceed.
- It enhances transparency and reduces risk of unauthorized actions through verification before fulfillment and an auditable log afterwards.
- It uses selective-disclosure credentials with key binding, not a UCP platform signature, as the verifiable format.
- It supports wider adoption of autonomous agents by giving merchants, agents and users a common way to prove what was agreed, when, and through which interaction.
Why intent must be verifiable
In traditional e-commerce, consent is visually explicit. A shopper navigates to a product page, adds items to a cart, reviews a summary, and clicks a clearly labeled confirmation. That visual journey inherently provides a trail of consent: items, pricing, shipping and billing choices, payment method, and a final action.
Agentic commerce removes most of that context. Interactions are fluid, multi-modal, and often lack persistent visual state. A request such as “buy those shoes” or “take care of the reorder” carries ambiguity about which item, what price, which address, and which payment instrument. The statelessness of conversational interfaces makes it difficult to reconstruct later what was actually approved.
Consider a scenario where an AI agent is tasked with managing a user’s investment portfolio. A compromised or confused agent instructed to rebalance holdings could place trades the user never meant to authorize, with significant financial consequences. The illustration shows why verification must happen before execution: each consequential action should be accompanied by a signed statement of intent that can be checked for authenticity, freshness and scope, and stored for later review.
Verifiable Intent addresses that gap. It transforms a high-level conversational request into a machine-readable, auditable commitment, and shifts assurance from post-transaction analysis to pre-transaction verification.
What Verifiable Intent actually is
Verifiable Intent was introduced on 5 March 2026, following pilots in February 2026. Mastercard developed the framework with Google, donated the work toward FIDO, and defined it around selective disclosure with key binding.
In practical terms, that means:
- The user’s approval is expressed as a SD-JWT with Key Binding under RFC 7800, which allows only the relevant claims for a transaction to be disclosed and binds them to a key held for that interaction.
- The format is not a UCP-signed object, not a UCP webhook payload, and not verified with a UCP platform public key.
- Any party can challenge a Verifiable Intent credential if it appears incorrect, expired, or misapplied.
- Challenges are resolved through existing chargeback and dispute processes, which review the linked approval, time and agent context.
For UCP readers, the implication is straightforward: do not implement Verifiable Intent as “UCP signs, merchant fetches UCP keys.” Implement it as an interoperable credential the agent obtains after explicit user approval, transmits with the commerce request, and the merchant verifies before fulfillment.
How Verifiable Intent relates to UCP and AP2
UCP orchestrates the commerce lifecycle — discovery, offer, cart, order and fulfillment messaging between agents and merchants. Verifiable Intent provides the proof that the user approved the consequential step within that lifecycle. AP2, where it applies, is a specialized payment layer for how payment credentials and mandates move. The three should not be conflated: UCP does not standardize Verifiable Intent, and Verifiable Intent mandates should not be described with AP2 payment vocabulary.
November 2026 update: UCP v2026-08-25 carries AP2 as the extension dev.ucp.common.payment.ap2_mandate for its autonomous-agent payment scenario; Verifiable Intent remains a separate Mastercard framework and is not standardized by UCP.
What a Verifiable Intent contains
A Verifiable Intent is a signed, challengeable approval expressed as an SD-JWT with Key Binding: only the relevant claims are disclosed and bound to a key for the interaction. No field-level payload schema is published in the sources verified for this refresh.
The Verifiable Intent lifecycle
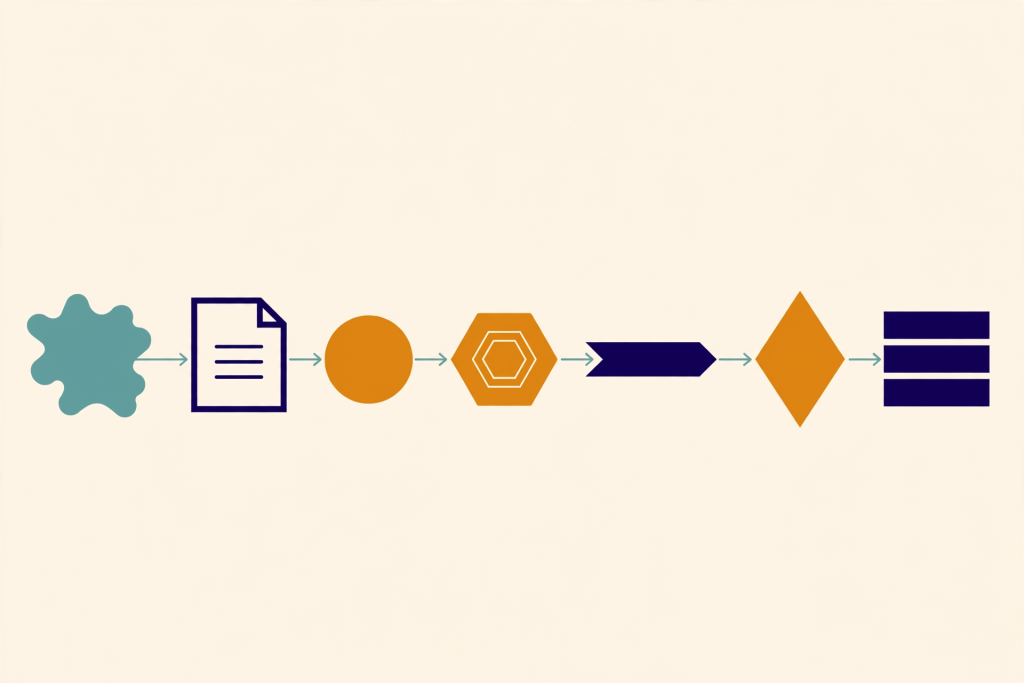
The journey from request to fulfillment follows a consistent flow, regardless of which commerce protocol carries it:
1. Intent expression
The user expresses intent in a structured way — through natural language refined by the agent, a graphical confirmation screen, or a machine-readable form — specifying the desired action, parameters and constraints.
2. Drafting and presentation for approval
The agent formulates that request into a structured proposal, such as an offer, cart or order proposal, drawing on known preferences only where appropriate. This is a critical human-in-the-loop step. The agent must present the proposal in plain language, highlighting total cost, items, delivery destination, payment choice and any fees, so the user understands exactly what approval would mean.
3. Explicit user approval
The user explicitly consents to the presented proposal — by voice confirmation, tap, biometric or other explicit action defined by the experience. Significant actions require explicit authorization; silent or inferred approval is not sufficient.
4. Signing
Upon approval, the intent is signed as an SD-JWT with Key Binding. The signature attests to the disclosed claims and binds them to the interaction, ensuring the payload has not been altered since approval.
5. Transmission to the merchant
The signed intent travels with the commerce request to the merchant backend for fulfillment, over the merchant’s secure commerce endpoint.
6. Verification before fulfillment
Before any fulfillment, the merchant verifies the credential: authenticity and integrity of the signature and key binding, freshness and expiration, merchant and amount alignment with internal records, and scope match to what was proposed. Only after successful verification does fulfillment proceed.
7. Auditable log
A record of the signed intent, verification outcome and resulting action is stored in an auditable log. That log supports dispute review, debugging and accountability, with access limited to authorized parties.
What agents and merchants must do
Agent-side responsibilities
- Formulate structured intent from conversational input, preserving specificity about action, amount and constraints.
- Present clearly with plain language and full details; avoid jargon and avoid bundling distinct approvals into one vague prompt.
- Require explicit authorization for significant actions and integrate with signing flows that produce the SD-JWT with Key Binding.
- Maintain state through drafting, presentation and signing, especially in multi-turn conversations, so retries do not create duplicate or divergent proposals.
Merchant-side responsibilities
- Provide a secure endpoint to receive signed intents, protected with appropriate authentication and rate limiting.
- Verify before acting — check signature and key binding, freshness, and business alignment such as merchant identity and totals.
- Enforce idempotency in fulfillment so network retries do not duplicate orders or actions.
- Handle errors robustly with detailed internal logging for verification failures and clear signals back so the agent can inform the user. Rigorous testing of verification, expiration and mismatch paths helps keep behavior predictable.
- Maintain audit trails of received intents and verification status. A detailed, immutable log of the user’s explicit intent and the rationale for each decision supports dispute resolution and debugging.
Security and trust model
By cryptographically linking a user-approved action to a specific agent interaction and time, Verifiable Intent improves accountability for all parties:
- Enhanced trust between users and agents, because consequential actions are tied to an explicit, checkable approval.
- Reduced risk of unintended or unauthorized actions, because verification happens before fulfillment rather than after.
- Increased accountability, because the auditable log makes it easier to identify what was approved and what was executed.
- Support for dispute review, because the stored approval, verification result and fulfillment record provide clear evidence of the agreed transaction for existing chargeback and challenge processes.
Implementing Verifiable Intent: best practices
- Clarity in presentation: highlight all critical details in the confirmation the user actually sees. Any ambiguity at this step undermines verifiability.
- Granularity and specificity: approve a specific proposal, not a general idea. Overly broad intents invite misinterpretation and dissatisfaction.
- Robust error handling: agents should explain signing or submission failures plainly and offer retry or adjustment; merchants should log verification failures with enough detail to diagnose cause without exposing sensitive data.
- Idempotency in fulfillment: deduplicate fulfillment retries so repeated submissions do not create duplicate orders.
- Scalability and performance: keep canonicalization and verification efficient for high-volume flows and integrate verification close to order acceptance.
- Audit-trail value: retain the full signed object and verification outcome according to retention policies, so consent can be demonstrated during later review.
Illustrative use cases
The following are illustrations of where explicit, verifiable approval matters, not verified deployments:
- E-commerce: an agent that finds options and completes a purchase only within pre-approved price, item and delivery parameters.
- Financial services: an agent that prepares trades or transfers tied to explicit per-action approval and limits.
- Supply chain: agents that negotiate or reorder within business rules, with each commitment traceable to an approved intent.
- Healthcare and regulated tasks: agents that schedule, request or share sensitive information only after clear approval and logging.
Verifiable Intent vs. traditional checkout
A browser checkout provides its own manifest: visible cart, pricing breakdown, addresses, payment choice and a definitive confirmation control. Each screen reinforces what is being agreed.
Agentic commerce lacks that scaffolding. Verifiable Intent fills the gap by structuring ambiguity into a precise commitment and requiring explicit confirmation after the agent has articulated full details. The signed credential then serves as the manifest that the visual page once provided.
Frequently Asked Questions
What is the core difference between a user prompt and Verifiable Intent?
A user prompt (‘buy me a jacket under $100’) is unauthenticated text; Verifiable Intent is a cryptographic delegation token signed by the user’s hardware passkey that mathematically enforces the $100 budget cap.
Why can’t merchants accept prompt text as proof of purchase authorization?
Prompt text cannot prove user identity, cannot prevent session tampering, and will be immediately rejected by credit card dispute committees in the event of an unauthorized purchase claim.
How does Verifiable Intent shift fraud liability away from merchants?
Card networks (Visa, Mastercard) recognize FIDO AP2 biometric attestation as conclusive cardholder authorization, automatically shifting chargeback liability to the card issuing bank under Compelling Evidence 3.0 rules.
Leave a Reply