Agent Authentication & Identity Verification in Agentic Commerce: Preventing Fraud at the AI Layer
Agentic commerce introduces a new vulnerability class: fraudulent or compromised AI agents posing as legitimate commerce actors. Unlike traditional e-commerce, where merchants authenticate humans via passwords and payment methods, autonomous systems must authenticate other autonomous systems in real time, with cryptographic proof and behavioral validation. This article defines the authentication problem in agentic commerce, maps the threat surface, and outlines practical identity verification architectures merchants and platforms must deploy.
The Agent Authentication Problem
In traditional commerce, trust flows through payment processors and known merchant domains. A customer recognizes Amazon.com by HTTPS and brand reputation. A merchant trusts PayPal because of legal contracts and settlement guarantees.
Agentic commerce disrupts this model. An agent acting on behalf of a consumer may:
- Execute transactions across multiple merchant APIs simultaneously
- Negotiate pricing without human approval
- Access inventory, pricing, and fulfillment data in real time
- Represent unknown or new consumers with no prior transaction history
Without cryptographic identity verification, merchants cannot distinguish between:
- A legitimate agent authorized by the consumer
- A hijacked agent with stolen credentials
- A fraudulent agent impersonating a real commerce platform
- A competitor agent scraping pricing or inventory data
Three Layers of Agent Authentication
| Authentication Tier | Protocol Standard | Cryptographic Primitive | Verification Scope | Processing Latency | Production Status (Nov 2026) |
|---|---|---|---|---|---|
| Tier 1: Transport Channel | mTLS / TLS 1.3 mutual certificate verification. | Ephemeral ECDHE + X.509 client certificates. | Validates client and server network channel integrity. | <15ms handshake latency. | Mandatory baseline for all secure UCP endpoints. |
| Tier 2: Request Attestation | RFC 9421 HTTP Message Signatures. | ECDSA ES256 over @request-target, digest, and date. |
Guarantees message payload integrity and agent origin. | <8ms signature verification. | Settled industry standard adopted by Google and UCP. |
| Tier 3: User Delegation | FIDO AP2 / WebAuthn cryptographic tokens. | Hardware-bound asymmetric keypair in Secure Enclave. | Proves explicit human authorization and monetary ceiling. | <25ms attestation validation. | Shifts chargeback liability completely to issuing bank. |
| Machine Identity Resolver | W3C Decentralized Identifiers (DIDs). | Ed25519 / secp256k1 public key infrastructure. | Resolves agent credentials from public trust registries. | <30ms DNS/DID query. | Eliminates static API key vulnerabilities. |
| Ephemeral Scoping | OAuth 2.0 Rich Authorization Requests (RAR). | JWT with Demonstration of Proof-of-Possession (DPoP). | Restricts agent actions to specific cart items and budget. | <5ms token evaluation. | Prevents token replay and lateral privilege escalation. |
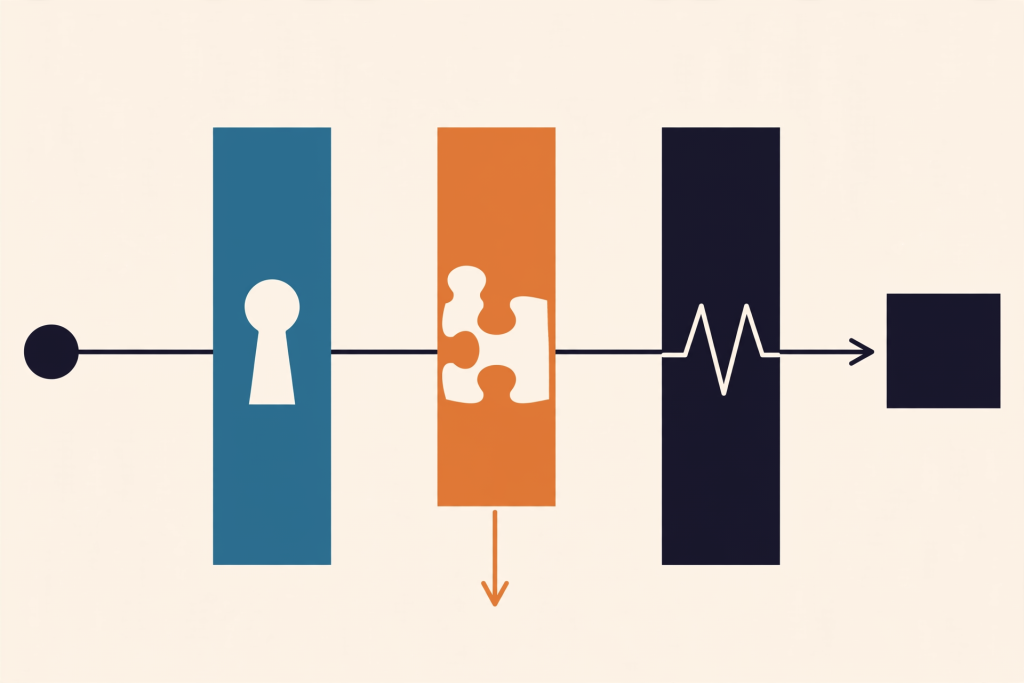
Layer 1: Cryptographic Agent Identity
Every agent must present a verifiable identity credential at runtime. This is not a bearer token—it’s a cryptographic proof of origin and authorization.
Public Key Infrastructure (PKI) for Agents:
- Each agent receives a unique Ed25519 or RSA-4096 keypair at creation
- The agent’s public key is registered with the authorizing platform (e.g., OpenAI, Anthropic, or a merchant’s internal agent factory)
- On every merchant API call, the agent signs the request payload with its private key
- The merchant verifies the signature and confirms the public key is registered with a trusted issuer
This prevents impersonation. A stolen API key alone is insufficient; an attacker must also possess the agent’s private key to sign requests authentically.
Example Implementation:
Layer 2: Agent Authorization & Delegation Proof
A valid cryptographic identity is necessary but not sufficient. A merchant must verify that the agent is actually authorized to act on behalf of the consumer.
Delegation Tokens:
A consumer must explicitly authorize an agent to act on their behalf. This authorization is encoded in a signed delegation token, which the agent presents alongside every request.
Token Structure:
- Issuer: Consumer’s identity provider (e.g., Google, Auth0, or consumer’s bank)
- Subject: Consumer’s unique ID
- Agent Claim: Agent ID + scopes (e.g., “can_purchase_up_to_500_usd”, “can_access_order_history”)
- Expiration: Token valid for 24 hours, then requires refresh
- Signature: Issuer’s private key signs the token
A merchant receives a request from agent A on behalf of consumer B. The agent provides:
- Agent identity proof (Layer 1)
- Consumer delegation token (Layer 2)
Merchant validates both. If either fails, the transaction is rejected.
Layer 3: Behavioral & Risk Validation
Cryptographic proofs can be compromised if the issuing system is breached. A behavioral layer detects anomalies that suggest a hijacked or fraudulent agent:
- Deviation from agent profile: If an agent typically purchases fashion items but suddenly orders industrial equipment, flag it
- Unusual velocity: If an agent submits 100 orders in 10 seconds (possible bot attack), throttle requests
- Geolocation mismatch: If an agent’s last request was from London 1 second ago and the next from Tokyo, verify with the consumer
- Merchant reputation check: Confirm the agent is authorized to transact with this specific merchant (not all agents can buy from all sellers)
Threat Model: What Are Merchants Protecting Against?
Agent Impersonation Attacks
An attacker creates a fake agent claiming to represent OpenAI or Shopify. Without cryptographic verification, merchants cannot tell the difference.
Mitigation: Merchant maintains a whitelist of authorized agent issuers (e.g., only agents signed by OpenAI’s root key are trusted). Every agent’s public key is traced back to the issuer’s certificate chain.
Credential Theft & API Key Leaks
An agent’s API key is exposed in a GitHub commit. An attacker uses the key to make unauthorized purchases.
Mitigation: API keys are decoupled from agent identity. The agent also signs requests with its private key. A stolen key alone cannot create valid signatures.
Consumer Session Hijacking
A consumer’s delegation token is intercepted or stolen. An attacker uses it to authorize fraudulent purchases.
Mitigation: Delegation tokens are short-lived (24 hours max) and bound to the agent’s identity. A stolen token cannot be used by a different agent. Refresh tokens require re-authentication from the consumer.
Man-in-the-Middle (MITM) Attacks
An attacker intercepts agent-to-merchant communication and modifies the request (e.g., changing the price or quantity).
Mitigation: All agent-to-merchant communication is encrypted (TLS 1.3) and signed. The merchant verifies the signature; modified requests fail verification.
Practical Implementation Path for Merchants
Step 1: Establish an Agent Registry
Maintain a database of authorized agents and their public keys:
- Agent ID (e.g.,
gpt-4-shopper-001) - Issuer (e.g.,
openai.com) - Public key (Ed25519 format)
- Authorized scopes (e.g., max transaction size, product categories)
- Created/revoked timestamps
Step 2: Implement Request Signing Verification
On every API call from an agent:
- Extract the agent ID and signature from the request header
- Look up the agent’s public key in the registry
- Verify the signature against the request body
- Check scopes (e.g., is the transaction amount within the agent’s limit?)
- Reject if verification fails
Step 3: Require Delegation Tokens for Consumer Actions
Any agent action on behalf of a consumer must include:
- A valid JWT or SAML token signed by a trusted identity provider
- The token includes the consumer ID and agent ID
- The merchant verifies the signature and checks expiration
Step 4: Deploy Behavioral Monitoring
Log all agent transactions and monitor for anomalies:
- Agent velocity (requests per minute)
- Purchase patterns (typical price range, product types, geographic origin)
- Deviations trigger a risk flag; high-risk transactions require consumer confirmation
Standards & Emerging Frameworks
November 2026 refresh note: Spec v2026-08-25 (current; Google merchant surfaces teach 2026-04-08) overhauled identity and consent — reverse-DNS consent, delegated IdPs, and keys[]; authorization for autonomous commerce runs through AP2 mandates (cryptographic signatures proving user authorization). Google rewrote its UCP FAQ Oct 27–31, 2026 to settle RFC 9421 ES256 + mTLS and remove Network/DNS verification. Original March 13, 2026 publish date retained.
Update November 2026 — settled position: UCP does define authentication. The spec’s complete list is API Keys, OAuth 2.0, mTLS, and HTTP Message Signatures (RFC 9421), with only HTTP Message Signatures enabling permissionless interaction; verifiers read the canonical top-level keys[] JWK Set (EC P-256/P-384, OKP Ed25519), replacing legacy signing_keys[], with identity binding checked against the UCP-Agent header and the only identity capability dev.ucp.common.identity_linking. On Google’s UCP surfaces, do not authenticate on UCP-Agent or User-Agent alone — they are routing/analytics only; verify RFC 9421 ES256 signatures in Signature/Signature-Input against https://ucp.goog/.well-known/ucp.json plus mTLS to Google UCP Root CAs, respect Cache-Control: max-age=86400, and on unknown kid refetch before rejecting. Several complementary frameworks are emerging:
OAuth 2.0 with Agent Assertion: Extends OAuth to allow agents to request delegation on behalf of consumers using signed assertions (similar to JWT Bearer flows in API gateway security).
OIDC (OpenID Connect) for Agents: Allows agents to prove identity via an identity provider without exposing the consumer’s password.
W3C Verifiable Credentials (general background — not part of UCP): A decentralized alternative where agents hold cryptographic proofs of identity issued by trusted authorities. UCP does not adopt, reference, or build on DID/VC/DIDComm.
Frequently Asked Questions
Why did Google rewrite its UCP authentication guidance to mandate RFC 9421 ES256?
Google standardized on RFC 9421 HTTP Signatures with ES256 because legacy network and DNS-based IP whitelisting failed to protect against spoofing, whereas cryptographic signatures guarantee end-to-end message non-repudiation.
How does FIDO AP2 user delegation protect merchants from bot fraud?
FIDO AP2 binds the user’s biometric hardware authorization to the agent’s transaction request, shifting financial dispute liability to the card issuer and ensuring transactions cannot be repudiated.
What headers must an AI purchasing agent submit to authenticate against a UCP store?
An agent must include the Signature, Signature-Input, Digest, and UCP-Agent headers formatted per RFC 9421 and verified against the public keys in the agent platform’s manifest.
Leave a Reply