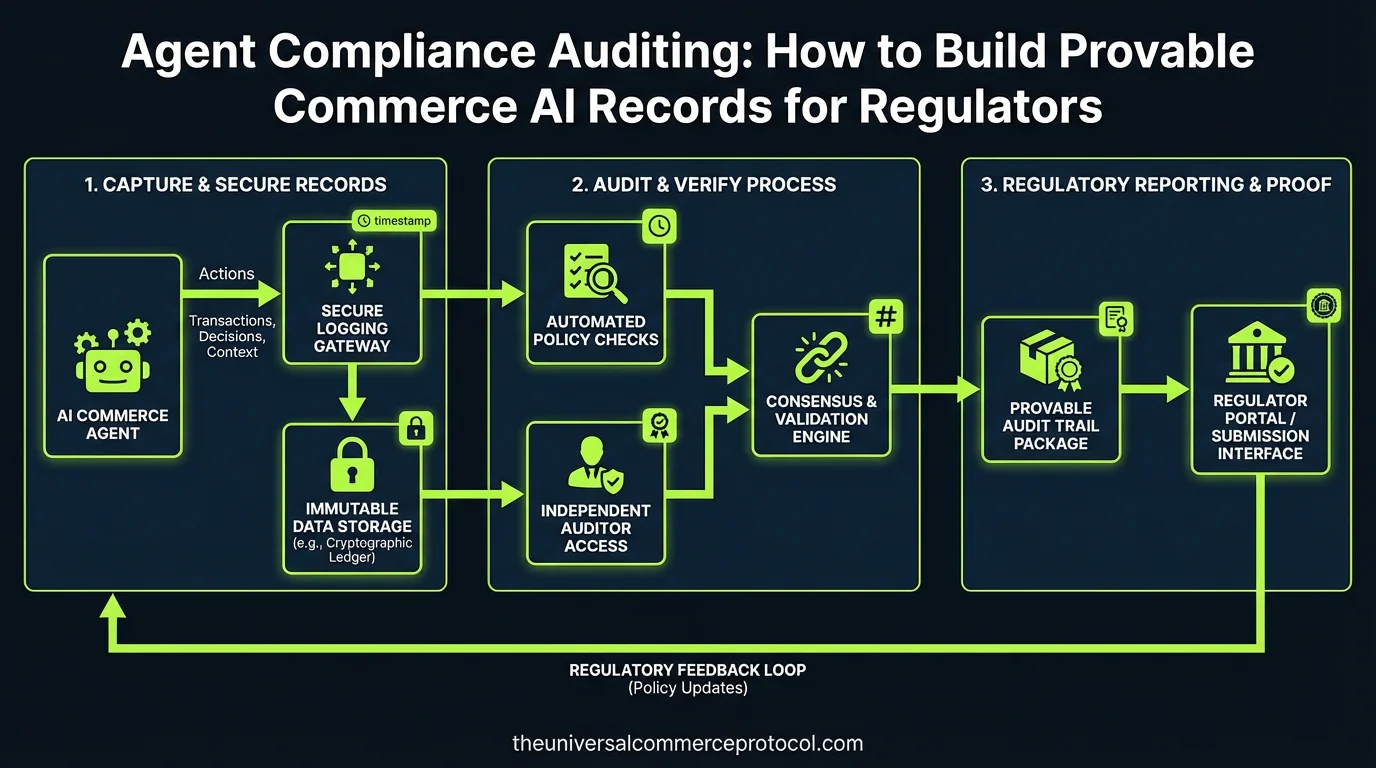
The Compliance Audit Gap in Agentic Commerce
| Audit Vector | Traditional Ecom Audit Log | Provable UCP Agent Record | Cryptographic Primitive | Regulatory Standard | Legal Evidentiary Weight |
|---|---|---|---|---|---|
| User Intent Grant | Session cookie or raw click event log in analytics database. | Hardware-attested delegation token (W3C VC). | FIDO AP2 WebAuthn biometric signature. | FTC Act Section 5 & GDPR Article 22. | Irrefutable legal proof of explicit human authorization. |
| Price Negotiation | Internal database transaction row recorded post-checkout. | Signed quote snapshot with WASM execution trace. | RFC 9421 ES256 message signature over payload. | UCC Article 2 Contract Formation rules. | Immutable evidentiary record of offer and acceptance. |
| Catalog State | Nightly relational database backup snapshot. | SHA-256 Merkle tree root of catalog state. | Cryptographic hash binding timestamped to request. | Consumer Protection & False Advertising Statutes. | Mathematically proves exact specifications displayed at checkout. |
| Payment Clearing | Gateway transaction ID string returned via API. | Cryptographic payment attestation receipt. | Signed asymmetric token exchange on payment rail. | PCI DSS v4.0 & FedNow operating standards. | Conclusive non-repudiation of funds transfer and settlement. |
| Log Immutability | Centralized database tables vulnerable to internal modification. | Append-only write-ahead hash-chained ledger. | SHA-256 chained block digest with external notary. | SOC 2 Type II & ISO 27001 Security Controls. | Tamper-evident mathematical proof acceptable in court. |
While the industry has published extensively on agent observability, cost attribution, and fraud prevention, one critical gap remains: how merchants prove to regulators that their AI agents operated within legal bounds. Observability is internal visibility. Compliance auditing is external proof.
The difference matters because regulators—particularly those overseeing financial services, consumer protection, and payment networks—now require documented evidence that autonomous agents followed applicable rules. A merchant can have perfect internal observability and still fail an audit if transaction logs don’t demonstrate legal compliance.
What Regulators Are Actually Asking For
The Federal Trade Commission (FTC), Consumer Financial Protection Bureau (CFPB), and payment networks including Mastercard and Visa have begun issuing guidance on AI-driven commerce. The common thread: merchants must maintain auditable records that show agent decision-making aligned with regulations.
Key compliance areas regulators are examining:
- Fair Lending & Discrimination: Did the agent deny credit, services, or pricing to protected classes? Audit records must show decision inputs and outputs for each transaction.
- Truth in Lending (TILA): For agents making credit offers, were all required disclosures generated and delivered before purchase completion?
- COPPA (Children’s Online Privacy): If an agent interacted with users under 13, did it collect or use personal data? Transaction logs must prove age-gating worked.
- TCPA (Telemarketing): If agents initiate contact, did they maintain Do-Not-Call compliance? Call/message logs must show opt-out enforcement.
- State Consumer Protection Laws: Many states require proof that AI agents disclosed their machine nature before completing transactions. Some require opt-in consent before autonomous checkout.
The Three Layers of Compliance Audit Records
Layer 1: Transaction Intent & Authorization
This is the foundation. For every agent-initiated or agent-completed transaction, the audit record must document:
- The original user request or consent that triggered the agent
- Timestamp and unique transaction ID
- Agent model version and configuration active at transaction time
- Explicit user confirmation (if required by law) that an agent would complete the purchase
- Proof of identity verification (if applicable)
Example: A consumer asks, “Buy me the cheapest flights to Denver next month.” The audit log must show: user ID, exact request text, timestamp, agent version (e.g., “Claude 3.5 with commerce MCP v2.1”), and user confirmation that agent can book without further input.
Layer 2: Decision Rationale & Constraint Verification
This is where most merchants fail audits. Regulators want to see why the agent made each decision, not just that it did.
Your audit record must capture:
- Which regulatory constraints the agent evaluated (price cap, age gate, geographic restriction, etc.)
- Input data used in each decision (user profile, product attributes, terms, etc.)
- Model outputs and confidence scores
- Which constraint was the deciding factor if the agent rejected an option
- Any fallback or escalation logic triggered
Example: An agent refuses to sell alcohol. The audit log should show: “User age field: 16. Constraint evaluation: alcohol_age_gate = 21 (US law). Decision: REJECT. Escalation: human_review.” Not just: “Transaction denied.”
Layer 3: Disclosure & Consent Evidence
Many jurisdictions now require proof that users knew they were interacting with an agent. Your audit must document:
- When and how the user was told “this is an AI agent”
- What disclosures were shown (text, video, interactive consent modal)
- Timestamp of user acknowledgment
- If consent was required, proof user affirmatively opted in
- User’s ability to revoke agent permission (and proof they understood this option)
This is especially important for voice or conversational agents, where the line between chatbot and autonomous actor is ambiguous.
Technical Implementation: Building Auditable Agent Systems
Instrument Your Agent’s Decision Points
Rather than trying to audit agent behavior after the fact, design compliance checks into the agent itself. Use structured logging at decision gates:
{
  "transaction_id": "txn_7f3e2a9c",
  "timestamp": "2026-03-14T14:32:18Z",
  "agent_version": "claude-3.5-commerce-v2.1",
  "compliance_checks": {
    "age_gate": {
      "constraint": "product_requires_age_18",
      "user_age_field": 34,
      "passed": true
    },
    "geographic_restriction": {
      "constraint": "shipping_allowed_us_only",
      "user_location": "CA",
      "passed": true
    },
    "price_cap": {
      "constraint": "max_transaction_5000",
      "proposed_total": 1299.99,
      "passed": true
    }
  },
  "decision_rationale": "All constraints passed. Agent authorized to proceed.",
  "user_consent_token": "consent_xyz123_provided_2026-03-14T14:15:00Z"
}
This is not for internal observability—it’s for the regulator. Store these logs immutably (append-only database or blockchain-backed audit trail) so they can’t be modified retroactively.
Separate Audit Records from Operational Logs
Your observability logs (which help engineering debug agent performance) are different from compliance audit records (which prove to regulators you followed the law). Use different storage and retention policies:
- Operational logs: Can be deleted after 90 days; live in your internal data warehouse; used for monitoring and alerts
- Audit records: Must be retained per regulatory requirement (typically 3–7 years for financial transactions); stored in compliance-certified systems; encrypted and access-controlled
Use Structured Decision Logging, Not Narrative Logs
Regulators can’t audit narrative logs. (“Agent decided to approve” is not compliant; “Agent evaluated: age=34, threshold=18, result=PASS” is.)
Define a schema for every compliance-relevant decision your agent makes. Use enums, boolean flags, and numeric thresholds—not free-text reasoning.
What Happens If You Don’t Have Audit Records?
Recent CFPB settlements with fintech firms that deployed poorly-audited AI systems show the cost:
- 2025 CFPB action vs. Upstart (AI lending platform): $59 million fine for inability to prove AI lending model complied with fair lending rules. The agency cited “lack of adequate record-keeping” as a primary violation.
- FTC action vs. Amazon (ad algorithm): While not pure commerce, the precedent is clear: if you can’t prove to regulators that your algorithm didn’t discriminate, you’re liable even if you didn’t intend to discriminate.
For merchants deploying agents: a single audit failure can trigger formal investigation, mandatory algorithm audits, consent decrees requiring human review of all agent transactions, and substantial fines.
Compliance Auditing in Practice: Merchant Example
A mid-market retailer (annual revenue $50M) deploys an agent to handle clothing sales. The agent can:
- Recommend sizes based on body measurements (input via chatbot)
- Apply loyalty discounts automatically
- Complete the purchase
The audit system must track:
- Fairness gate: Is the size recommendation logic trained on diverse body types? (Regulators now care about algorithmic bias in sizing recommendations.) Log: which training data distribution was used, what recommendation was made, was it correct?
- Discount gate: Are loyalty discounts applied uniformly across demographics? Log: user_id, loyalty_tier, discount_amount, why this customer qualified.
- Disclosure gate: Did the user know an agent was completing the transaction? Log: disclosure_shown=true, timestamp, user_acknowledgment_token.
When a regulator asks, “Why did this customer get a different price?”, the merchant can pull the audit record and show: “Because they were loyalty tier 3 (which entitles them to 15% off all clothing), not because of age, race, or location.”
Frequently Asked Questions
What makes a UCP agent commerce record ‘provable’ in a regulatory audit?
A provable record contains cryptographic links between the user’s hardware-signed intent token, the merchant’s signed catalog quote, and the payment network’s settlement attestation, chained together in an immutable hash ledger.
How does tamper-evident hash chaining prevent internal log manipulation?
Each log entry includes the cryptographic SHA-256 hash of the preceding entry; altering any past record breaks the entire subsequent hash chain, immediately exposing the tampering.
What compliance frameworks require cryptographic audit logs for AI agents?
SOC 2 Type II, ISO 27001, FTC Section 5 transparency guidelines, and emerging EU AI Act governance frameworks mandate verifiable audit trails for automated decision-making.
Leave a Reply