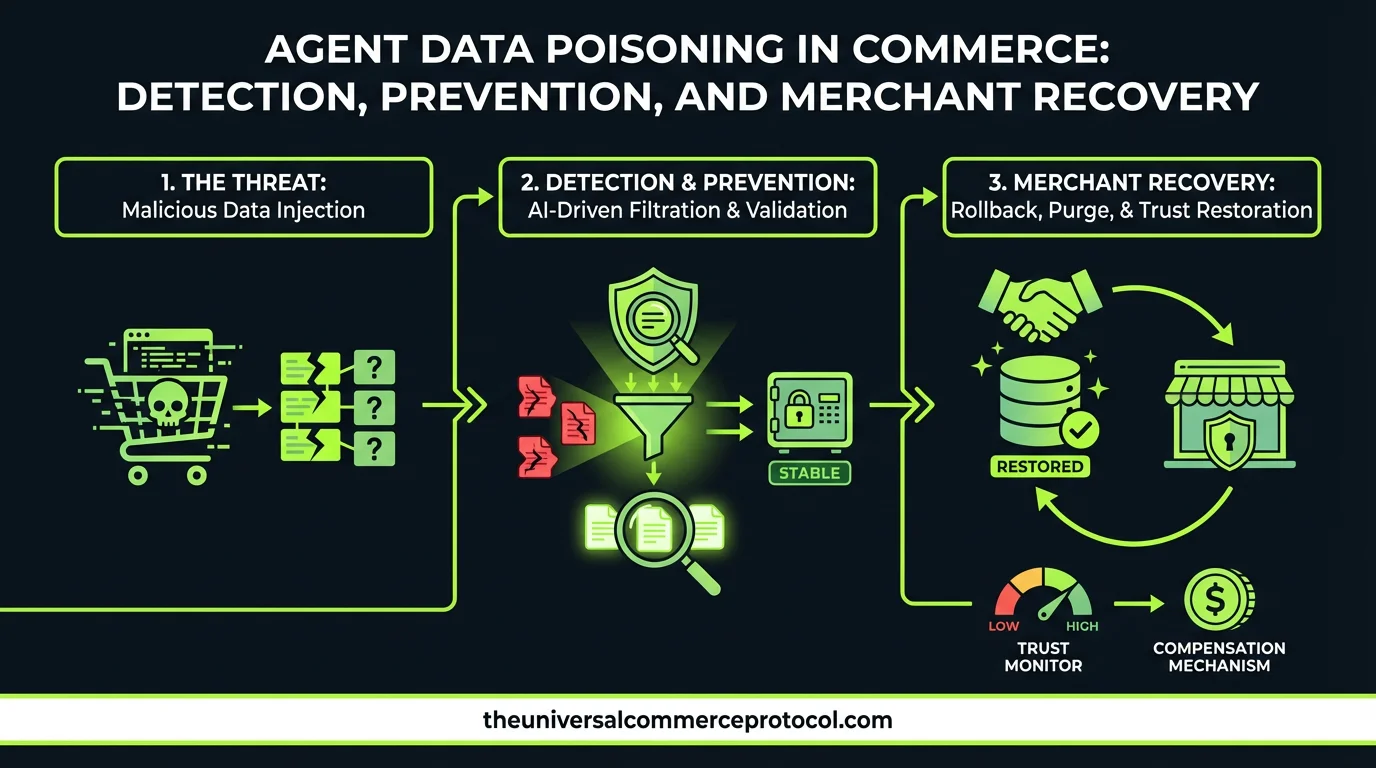
The Data Poisoning Risk in Agentic Commerce
As AI agents become economic actors—making autonomous purchase decisions, negotiating supplier terms, and managing inventory—they inherit a critical vulnerability: the systems that train and inform them can be compromised.
Data poisoning attacks inject malicious or corrupted information into the datasets and real-time feeds that agents rely on. Unlike traditional fraud, which targets transactions or accounts, poisoning targets the agent’s decision-making foundation itself.
A competitor could flood an agent’s training data with inflated pricing signals. A supplier could inject false demand forecasts to drive overstock. An attacker could corrupt product quality ratings to push agents toward inferior vendors. The agent, acting on poisoned information, makes decisions that appear legitimate—but systematically favor attackers.
How Data Poisoning Corrupts Agent Decisions
Agentic commerce agents ingest multiple data streams: product catalogs, inventory levels, pricing feeds, supplier performance metrics, customer behavior, and market intelligence. Each stream is a potential poisoning vector.
Supply-side poisoning: A supplier modifies their API response to inflate inventory availability, knowing the agent will over-order at margin-thin prices. The merchant discovers overstock weeks later.
Competitive poisoning: A rival submits fake reviews or quality scores for a product, degrading its agent-assigned preference score. Sales shift to the competitor’s equivalent product.
Training data poisoning: Attackers inject historical transaction records with manipulated customer preferences or artificially successful pricing points during the agent’s training phase. Once deployed, the agent systematically misallocates budget.
Real-time feed poisoning: Man-in-the-middle attacks or compromised APIs deliver corrupted demand signals, competitor pricing, or cost data. Multi-turn agents compound errors as they make decisions based on poisoned outputs from previous turns.
Why Existing Safeguards Fail
Traditional data validation—schema checks, range limits, anomaly detection—catches obvious corruption. Poisoning attacks don’t.
A poisoned pricing feed might deliver values that are statistically plausible but systematically biased toward a competitor. An inventory signal might be internally consistent but shifted 10% high. A customer preference vector might be subtle enough to pass statistical tests but push agent allocation in a profitable (for the attacker) direction.
Agents trained on large, complex datasets lack transparency into which features drove which decisions. A merchant cannot easily ask: “Why did the agent prefer Supplier A over Supplier B?” without explainability tooling. Without that visibility, poisoning goes undetected until financial impact surfaces.
Detection Strategies for Poisoned Agents
Comparative benchmarking: Run the same agent on clean historical data and on current data. Compare decision distributions. If the agent’s supplier selection, pricing, or inventory behavior has shifted materially without a business justification, poisoning is a candidate hypothesis.
Adversarial input testing: Deliberately inject known-false data into the agent’s inputs (in staging) and monitor decision changes. Poisoned agents will shift behavior predictably toward the attacker’s goal. Clean agents treat false inputs as noise.
Data source validation: Cryptographically sign all inbound data feeds (APIs, catalogs, pricing). Any unsigned or invalid signature indicates a compromise. Cross-reference feeds with multiple independent sources; if one diverges, isolate it.
Decision audit trails with explainability: Log not just what the agent decided, but why. Which features, weights, and inputs drove the decision? Poisoning often creates explainability anomalies—decisions that rely on unexpected features or contradict historical patterns.
Behavioral baselines: Establish normal agent behavior: typical supplier diversity, price variance, inventory turnover. Poisoning often narrows diversity (favoring one supplier) or shifts price/inventory patterns. Significant deviation triggers investigation.
Prevention Architecture
Data source isolation and attestation: Require all external data sources to provide cryptographic proof of origin and integrity. Use merkle trees or blockchain-style hashing to make tampering detectable. Never accept unsigned feeds.
Redundant sourcing: For critical inputs (pricing, inventory, demand), source from multiple independent providers. An agent should cross-check signals; if one source diverges from others, flag and investigate.
Staged rollout for new data sources: Before adding a supplier API or market data feed, run it in parallel with existing sources for 2-4 weeks. Measure for bias, correlation anomalies, or unusual decision shifts before full integration.
Model retraining frequency: Poisoned training data creates persistent agent bias. Retrain models frequently (weekly or bi-weekly) on fresh data to reduce the window in which old poisoning remains active. Maintain version control; if poisoning is detected, rollback to the last known-good model.
Agent sandboxing: In high-risk scenarios (large orders, new suppliers, significant spend), require agent recommendations to pass human approval or a second-stage validation system before execution.
Recovery and Remediation
Data forensics: When poisoning is suspected, audit all inbound data feeds for the suspected time window. Identify which sources were compromised, what values were corrupted, and which agent decisions relied on that data.
Decision reversal: Transactions made by poisoned agents may need reversal. Work with suppliers to identify orders that were over-executed due to false inventory signals. Negotiate returns or credits. For supplier negotiations, review contracts signed by agents; if poisoning influenced terms, renegotiate.
Vendor accountability: If a supplier’s API was compromised, require them to provide signed attestations of data integrity going forward. Consider contractual penalties for data source compromise. For third-party data providers, similar terms should apply.
Model retraining on sanitized data: Remove all data from the poisoning window from training sets. Retrain models on clean historical data. Validate the retrained model against known-good benchmarks before re-deployment.
Incident communication: Inform customers and partners of any agent decisions that may have been affected. Transparency protects merchant reputation and builds trust in agentic commerce systems.
FAQ
Q: How do I know if my agent has been poisoned vs. just making bad decisions?
A: Poisoning creates systematic, directional bias (favoring specific suppliers, price points, or strategies). Bad decisions are random or inconsistent. Compare agent behavior across time; poisoning shows correlated shifts that favor a particular party.
Q: Should all agents have explainability built in?
A: Yes. Without explainability, you cannot audit decisions or detect poisoning. For agents making autonomous decisions above a certain spend threshold, explainability is non-negotiable.
Q: Can blockchain solve data poisoning?
A: Blockchain ensures tamper-evident data provenance, not data accuracy. A supplier can still provide false but cryptographically signed data. Blockchain is a component of defense, not a complete solution.
Q: What’s the cost of undetected poisoning?
A: Varies widely. A poisoned inventory agent might drive 5-15% overstock cost. A poisoned pricing agent could erode 2-8% margin. Supplier favoritism could lock merchants into unfavorable long-term contracts. Early detection is far cheaper than discovery through financial reporting.
Q: Should I run multiple agents in parallel to detect poisoning?
A: For critical decisions, yes. Running two independent agents on the same problem and comparing outputs is expensive but effective for high-value scenarios (major supplier selection, large capital allocation). For routine decisions, single-agent operation with strong data validation suffices.
Q: How does agent state management complicate poisoning recovery?
A: Multi-turn agents carry state across decisions. Poisoning in turn 1 influences decisions in turn 2-N. Rollback requires not just reverting decisions, but unwinding the entire decision chain. This is why versioned agent snapshots and regular state audits are critical.
| Parameter / Field | Type | Requirement | Constraint | Description | Example |
|---|---|---|---|---|---|
detection.forensic_sanitization_pipeline |
enum |
Mandatory | STATISTICAL_ZSCORE | MERKLE_PROVENANCE | GRAPH_NEURAL_NET | Forensic inspection pipeline analyzing inbound product feeds for anomalous patterns and malicious tampering | "MERKLE_PROVENANCE" |
quarantine.automated_isolation_threshold |
float |
Critical | Confidence >= 98.5% | Statistical anomaly confidence score triggering immediate isolation and blacklisting of offending data sources | 99.2 |
attestation.tamper_evident_catalog_seal |
enum |
Mandatory | SHA256_RSA4096 | ED25519_MERKLE_ROOT | Cryptographic seal applied to master product feeds ensuring zero intermediate alteration during transit | "ED25519_MERKLE_ROOT" |
monitoring.realtime_feed_drift_window_minutes |
integer |
Standard | 1 <= window <= 60 minutes | Evaluation window over which catalog pricing velocity is checked against standard deviation historical bands | 15 |
consensus.byzantine_price_oracle_nodes |
integer |
Optimal | >= 5 independent validator oracles | Minimum number of independent market oracles required to confirm fair market price before order approval | 7 |
resilience.poisoned_feed_recovery_time_sec |
integer |
Mandatory | <= 30 seconds | Mean time to recover (MTTR) by reverting catalog indices to last known uncompromised snapshot | 8 |
Frequently Asked Questions: AI Agents & Autonomous Commerce
Q1: What methods are most effective for detecting data poisoning in real-time commerce feeds?
Effective architectures combine Merkle tree provenance validation (ensuring uncorrupted origin data) with statistical Z-score outlier detection and Graph Neural Networks (GNNs) that flag coordinated pricing anomalies.
Q2: How do Byzantine price oracles safeguard buyer agents from manipulated listings?
Rather than trusting a single merchant feed, buyer agents cross-reference pricing across a minimum of 5–7 independent decentralized validator nodes, rejecting any bid that deviates by more than 2 standard deviations from consensus.
Q3: What automated actions occur when an inbound catalog feed is flagged as poisoned?
The security gateway immediately isolates the data source, revokes API authorization tokens, reverts local product embeddings to the last verified snapshot within 30 seconds, and generates an alert for security teams.
by
Tags:
Leave a Reply